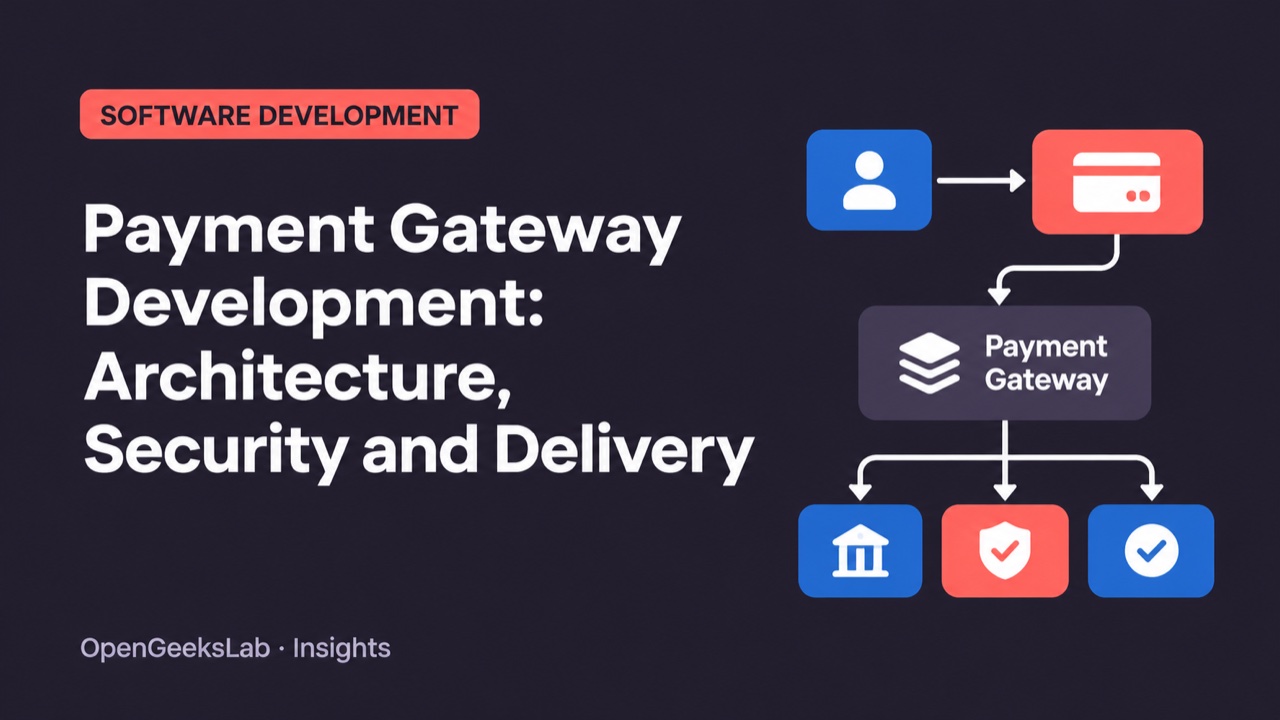
Direct answer: Most businesses should integrate a regulated payment provider rather than build a card gateway from scratch. The product still needs careful architecture around payment state, idempotency, webhooks, fraud, refunds, reconciliation and customer support. Building core acquiring or gateway infrastructure is a different, regulated undertaking.
Clarify what “payment gateway” means
The term can describe a hosted checkout, a provider API, an orchestration layer across processors, or the regulated infrastructure that moves authorization messages. These have radically different risk, cost and compliance scope.
For an ecommerce or SaaS product, the usual goal is a reliable payment integration: collect payment details through provider-controlled components, create a payment, respond to asynchronous updates, grant the correct entitlement and reconcile provider records with internal orders.
A typical payment flow
- The server creates an order and a provider-side payment object with a unique internal reference.
- The client uses hosted fields or a provider SDK to collect sensitive payment details.
- The provider handles required customer authentication and returns an intermediate result.
- The application waits for an authoritative server-side status or signed webhook.
- The order state and financial ledger update atomically or through a recoverable process.
- Reconciliation compares internal records with provider reports and settlements.
Provider APIs often model a payment as a state machine because authentication and settlement are not always immediate. Stripe’s Payment Intents documentation is one example of this pattern.
Keep the card-data boundary small
Use hosted checkout or tokenized provider components where possible so raw card data does not pass through your application. Exact obligations depend on the integration and business. The PCI Security Standards Council publishes the current standard and supporting material in its PCI DSS document library.
Compliance is not a replacement for secure engineering. Protect API credentials, validate callbacks, rotate secrets, restrict admin actions, patch dependencies, log security events and test incident procedures.
Design for idempotency and retries
Networks fail after a request succeeds. A client or worker may retry without knowing whether money moved. Every payment-changing operation needs a stable idempotency key and a rule for duplicate messages. Webhook processing should record event identifiers before applying business effects.
Do not treat webhook order as guaranteed. Retrieve authoritative provider state when events arrive late or appear inconsistent.
Separate payment state from order state
An order can be awaiting payment, paid, partially refunded, cancelled or disputed. A payment attempt can be created, require action, fail, succeed or be reversed. Keeping these models separate makes retries and multiple payment methods manageable.
Use a ledger for financial truth
Balance-changing events should be append-only and traceable. Store amounts in minor currency units, preserve currency, record provider references and never calculate financial history from mutable status fields alone. Reconciliation must identify missing, duplicated or mismatched transactions and assign an owner to resolve them.
Plan refunds, disputes and support
The customer experience includes more than checkout. Build tools for refund eligibility, partial refunds, dispute evidence, failed-payment recovery, receipt lookup and support-safe diagnostics. Sensitive admin actions need stronger authorization and audit history.
Build versus integrate
Integrate a provider when payments support the product but are not the product. Build an orchestration layer when routing, multiple providers, regional payment methods or unified reporting creates clear value. Consider core gateway infrastructure only with the regulatory, security, banking and operational capability to run it continuously.
OpenGeeksLab’s API integration guide explains resilient boundaries, while custom software development can connect checkout, orders, billing and back-office systems. For a new product, use the MVP scope and cost guide before committing to multi-provider complexity.
Frequently asked questions
Can we build our own payment gateway?
Technically yes, but regulated payment infrastructure requires security, compliance, banking relationships, monitoring and operations beyond a normal checkout integration.
What should an MVP include?
One provider, one primary payment method, reliable order state, signed webhooks, idempotent retries, refunds, receipts, monitoring and reconciliation.